Security Engineer · Salt Lake City
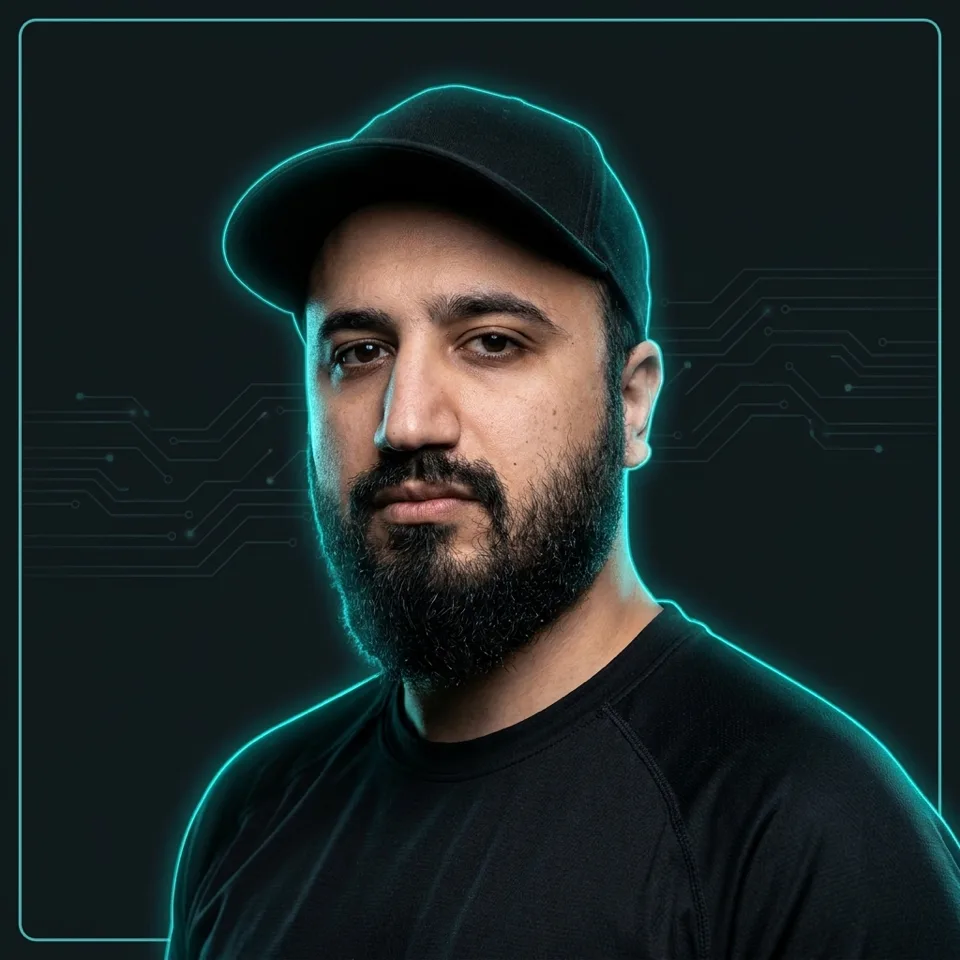
Mohammed Alrashid
I secure a cloud-native building automation platform.
At PassiveLogic, I own vulnerability management, identity and access, email security, and incident response across GCP, Azure, Entra ID, and on-premises infrastructure. I'm interested in zero trust and in how systems break, so I can make them harder to break.
- GCP / Azure
- Entra ID / Conditional Access
- Rapid7 InsightVM
- Wiz CSPM
- Defender for Office 365
- Incident response
- Platform risk reviews
- Firewalls / VPN / VLANs
- SOC 2 / GDPR evidence
What I work on
My day-to-day work is security engineering: vulnerability management, identity and access, incident response, and reviewing internal platforms before release. I'm building pentesting skills so I can test the systems I defend more deeply. My home lab gives me room to try things, break them, and work out why.
- Cloud security
- IAM
- Incident response
- Zero trust
- Learning pentesting
- Home lab
At PassiveLogic since 2023
Security Engineer
Feb 2024 - PresentPassiveLogic
- Own vulnerability management end to end: authenticated Rapid7 InsightVM scanning across cloud, server, and endpoint environments, severity-based SLA tracking, and patch campaigns through Jamf and Intune.
- Run CSPM with Wiz across GCP and Azure, and lead identity on Entra ID and GCP: SAML and OIDC federation, SCIM provisioning, workforce identity federation, and Conditional Access with MFA.
- Run email security in Microsoft Defender for Office 365 and lead incident response from detection through postmortem; review internal platforms for risk before release; own SOC 2 and GDPR control evidence.
Security Intern
Aug 2023 - Dec 2023PassiveLogic
- Established the company's first documented cloud security controls across GCP, Azure, and Microsoft Exchange.
- Assessed cloud and network security posture, managed vulnerabilities, and administered IAM in GCP and Azure Active Directory toward least privilege.
Lab, tools, and notes
Home lab
Proxmox, segmented networks, backups I can restore, and local AI. I use it to learn by doing.
Read about the labSecurity tools
A secret generator, a subnet calculator, and a self-hosted copy of CyberChef. They all run in your browser.
Open toolsNotebook
Notes on zero trust, cloud security, AI agents, and the parts of security I want to understand better.
Read the NotebookLet's talk
If you have a security role, a project, or just a question, I'd like to hear from you.
Get in touch